Zimbabwe has a Data Protection Authority
Under the Cyber and Data Protection Act [Chapter 12:07], the Postal and Telecommunications Regulatory Authority of Zimbabwe (POTRAZ) is designated as Zimbabwe's Data Protection Authority.
The Authority is responsible for regulating how personal information may be processed and enforcing fair and lawful data processing practices.
The law applies to processing and storage of data, including processing carried out through automated systems.
Businesses therefore need to take data protection seriously when implementing software that stores information about identifiable individuals.
Read the Cyber and Data Protection Act [Chapter 12:07]
Do companies need a data controller licence?
The answer can be yes.
The 2024 Cyber and Data Protection Regulations provide that a person who determines the purposes and means of processing personal data must apply for a data controller licence.
The regulations also cover people who decide what personal data is collected, from whom it is collected, or who process personal information for commercial gain or another benefit.
A data controller licence is valid for 12 months and is subject to renewal and continued compliance with the applicable legislation and licence conditions.
The regulations establish four licence tiers based on the number of data subjects processed.
This means that a business cannot simply assume that because it uses a third-party software platform, its own data protection responsibilities disappear.
The business still needs to understand its role as a data controller and how its data processors and technology providers handle personal information.
Read S.I. 155 of 2024 — Data Controller Licensing Regulations
What happens when your data is stored outside Zimbabwe?
This is particularly important for businesses using cloud software.
Zimbabwe's Data Protection Act contains specific provisions dealing with the transfer of personal information outside Zimbabwe.
Section 28 states that a data controller may not transfer personal information to a third party in a foreign country unless an adequate level of protection is ensured in that country or international organisation and the transfer is for purposes falling within the controller's competence.
The assessment of adequacy takes into consideration factors including:
The nature of the personal data
The purpose and duration of the processing
The country receiving the information
Data protection laws applicable in that country
Professional rules and security measures applicable to the processing
So the issue is not simply whether a server is physically located outside Zimbabwe.
The important question is whether the international transfer and processing arrangement satisfies the requirements of Zimbabwe's data protection framework.
The Act also provides circumstances in which transfers to countries that do not provide an adequate level of protection may take place, including certain situations involving consent, contractual necessity, legal requirements and important public-interest grounds.
Read Section 28 and 29 of the Data Protection Act
POTRAZ also asks where your data is located
The practical importance of data location can be seen in POTRAZ's own Data Controller Licence application form.
The form asks applicants to indicate their data processing location, including whether their data is located in Zimbabwe and, if it is not, the country where it is located.
The form also asks applicants about their data processors and whether written data processing contracts exist.
For businesses, this means your software architecture and storage arrangements are not merely technical decisions. They can form part of your data protection and compliance considerations.
View the POTRAZ Data Controller Licence Application Form
Security is also part of compliance
Data location is only one part of the picture.
The 2024 regulations require appropriate technical and organisational measures to protect the security, integrity and confidentiality of personal information.
The regulations specifically refer to measures designed to maintain the security, confidentiality, integrity and availability of systems and personal data.
They also require measures that allow access to personal data to be restored in a timely manner following a physical or technical incident.
In other words, a business needs more than a database somewhere on the internet.
It needs appropriate security, controls, availability and recovery measures.
Where does CompanyOp fit in?
This is where CompanyOp is designed to make life easier for Zimbabwean businesses.
CompanyOp provides connected business applications for accounting, payroll, POS, inventory, loan management, client background checks, contracts, recruitment, property management, fiscalisation and other business processes.
Instead of buying completely separate systems for every department, businesses can operate multiple applications inside one company workspace.
But we also recognise that not every organisation has the same data protection requirements.
You can use your own storage
For organisations that have their own data controller arrangements, internal IT policies or specific storage requirements, CompanyOp can be configured to work with customer-controlled storage.
This gives organisations greater control over where their business documents and personal information are stored.
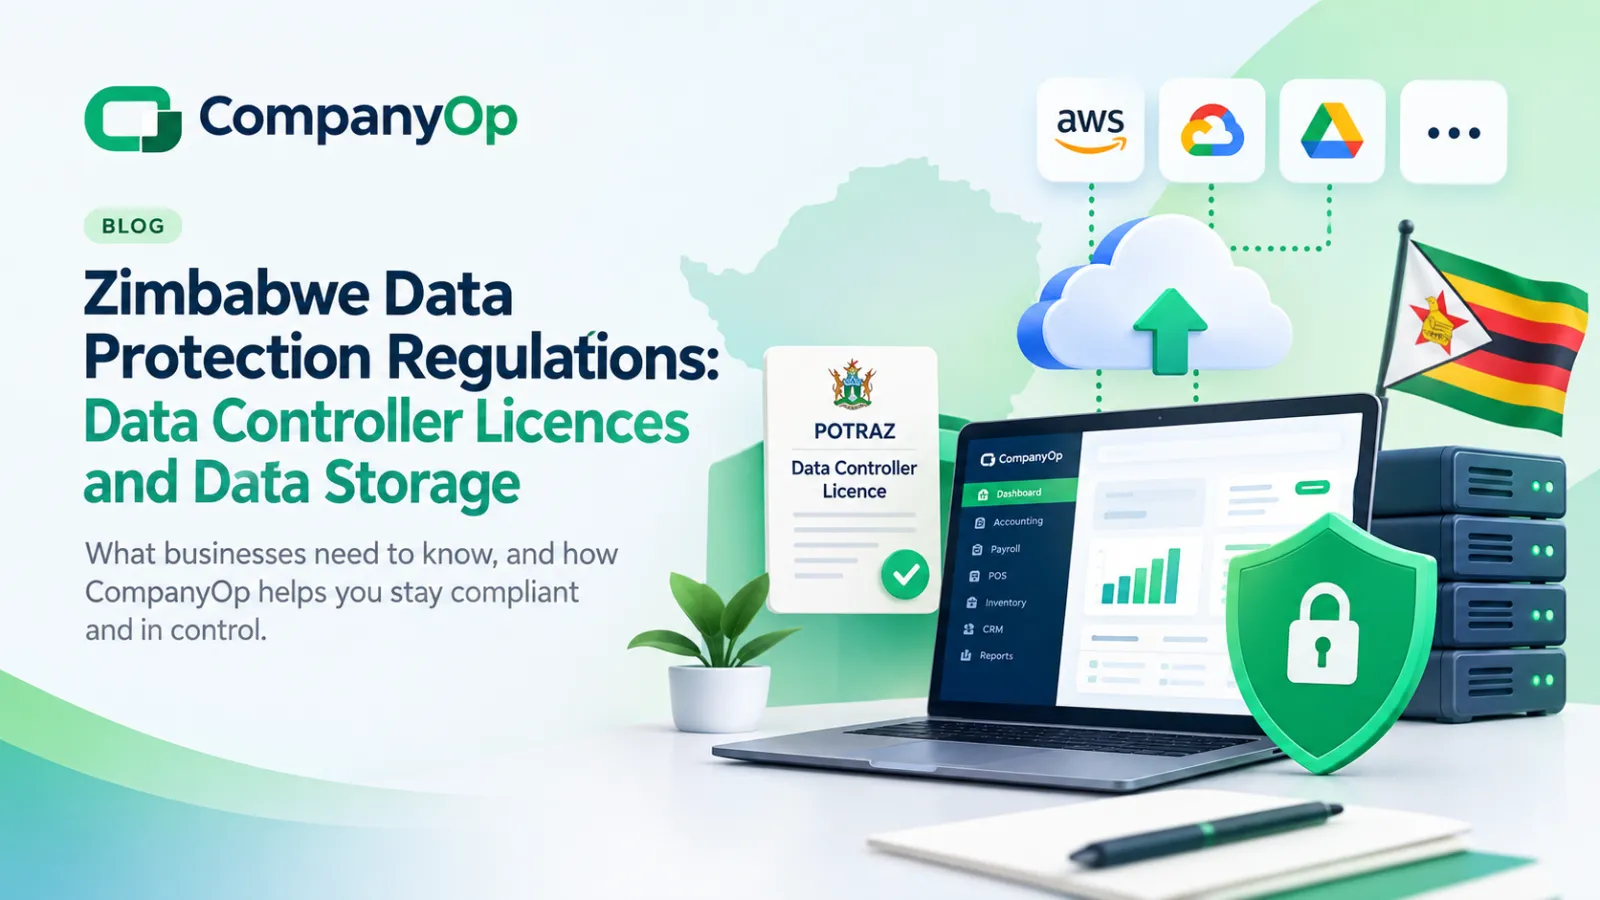
CompanyOp supports storage integrations including:
Amazon S3
Google services
Google Drive
Other supported storage configurations
For example, a company that already maintains its own approved Google Drive or Amazon S3 environment can use that storage rather than treating the software platform as the only place where its documents must reside.
This can be particularly useful for organisations with their own IT infrastructure, compliance requirements or data governance policies.
You control the storage. CompanyOp provides the business software.
Or let CompanyOp handle the storage
Not every business wants to become an IT infrastructure company.
A small business owner wants to run the business, not spend Saturday morning configuring buckets, access policies, backups and storage permissions.
That's why CompanyOp also provides managed application infrastructure for businesses that want a simpler approach.
Your business can use CompanyOp to run its operations while we take care of the underlying application environment, security controls, backups and infrastructure.
The result is a much simpler model:
Choose the apps you need.
Run your business.
Let CompanyOp handle the technology.
CompanyOp's modular approach means you can start with the applications you actually need and add more as your business grows.
For example, a business might start with Accounting, then add Payroll, POS, Inventory, Contracts or other applications as its requirements change.
See CompanyOp applications and pricing
Data protection is a shared responsibility
There is an important distinction businesses should understand.
Using compliant technology does not automatically make a company compliant with every requirement of Zimbabwe's data protection laws.
Your business may still have responsibilities as a data controller, including understanding what personal information you collect, why you collect it, how it is processed, who processes it, where it is stored and what safeguards are in place.
CompanyOp's role is to provide technology and storage options that can support those requirements.
Your organisation remains responsible for its own legal and regulatory obligations, including obtaining any licence that applies to it.
A better way to think about business software
For many Zimbabwean businesses, software used to be viewed simply as a tool for accounting, payroll or managing customers.
That is changing.
Modern business software also needs to answer questions about:
Who has access to the data?
Where is the data stored?
Who processes it?
How is it protected?
Can it be recovered after an incident?
Can the organisation control its storage environment?
Those questions matter when your software contains customer information, employee records, financial information, KYC documents, borrower information or other personal data.
CompanyOp is built with this reality in mind.
Whether you want managed infrastructure or want to connect your own storage environment, you can use CompanyOp as the operating system for your business while maintaining a storage approach that fits your organisation's requirements.
Run your business. Keep control of your data.
Zimbabwe's data protection framework is becoming an important consideration for businesses of every size.
You do not necessarily need to build your own ERP system to maintain control over your business data.
With CompanyOp, you can choose the business applications you need and, where required, use your own supported storage environment. Or, if you simply want everything managed for you, CompanyOp can provide the infrastructure and storage environment so you can focus on running the business.
Your business. Your data. Your choice of storage.
Explore CompanyOp and start with the apps your business actually needs.
Important note
This article is provided for general information and does not constitute legal advice. Data protection obligations can depend on the nature of the organisation, the categories of personal information processed, the organisation's role as controller or processor, the location of processing and applicable regulatory requirements. Businesses should obtain professional advice and confirm their specific obligations with the Data Protection Authority where necessary.